A general section to talk about AI Agent Security
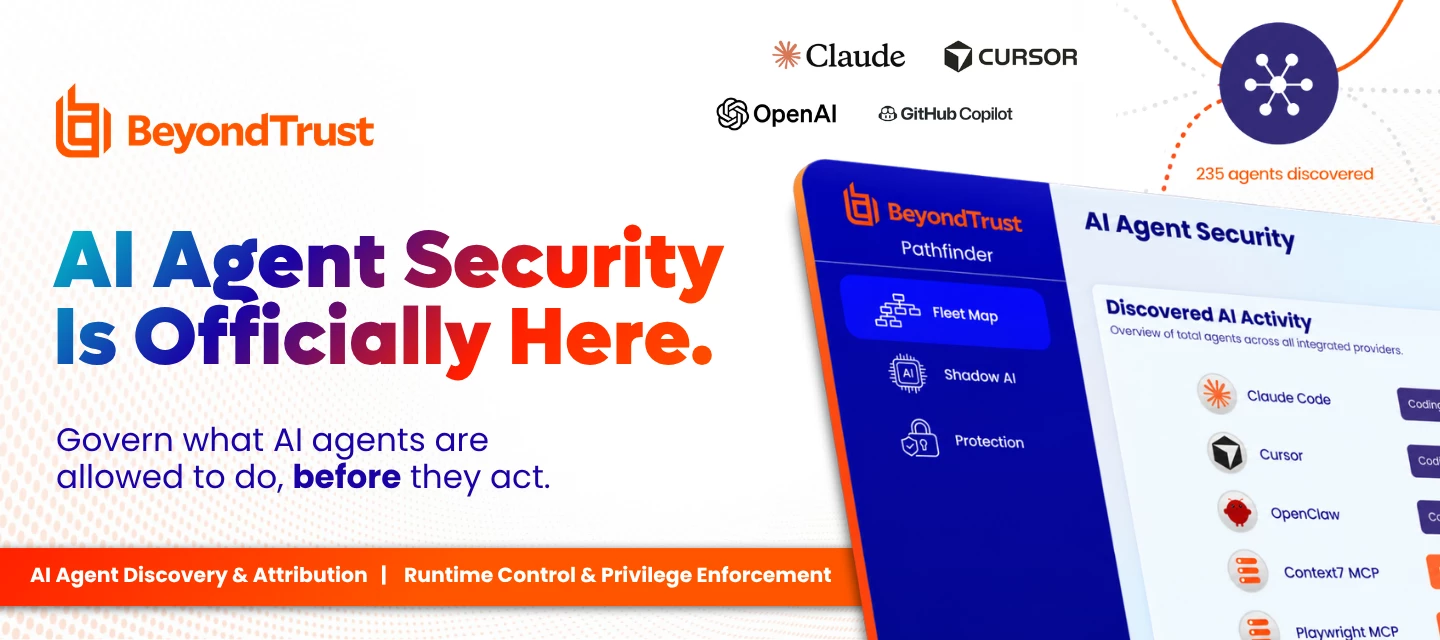
We believe organizations should be able to embrace AI productivity without becoming a victim to the unintended damage of AI actions. BeyondTrust AI Agent Security makes that possible. Building on BeyondTrust’s market-leading Endpoint Privilege Management and 20 years of privilege-centric identity security, our approach to AI security focuses not only on what is malicious, but also on what is permitted. Purpose-built for agentic AI on the endpoint, AI Agent Security distinguishes AI agent activity from human activity and governs what agents are allowed to do before they act, without restricting their human users, helping organizations safely embrace AI at scale. How our early access customers are already using AI Agent Security:AI Agent Discovery & Attribution: Identifying all the AI agents running across their endpoints, including shadow AI, sub-agents, Skills, and MCP servers; and attributing every action to its source, human or agent. Vendor-Agnostic Governance: Applying consi
Already have an account? Login
Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.