Apprentice
December 5, 2025
Solved

CVE-2023-49944/BT 23-08

  • December 5, 2025
  • 4 replies
  • 245 views

Does anyone know how to implement this remediation - the instructions are very vague. 
BT23-08 | BeyondTrust

    Best answer by Jens Hansen

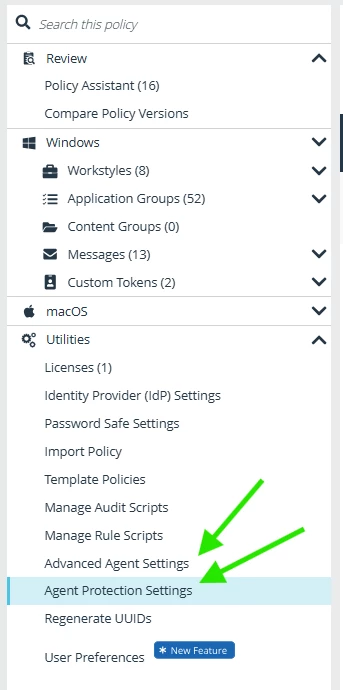
    As stated in the BT-23-08, Make sure that Anti-Tamper is enabled and also that you have Agent Protection enabled.

    As this will require true local Admin the Agent Protection is key for avoiding Admin users to gain access also, Anti-Tamper will take care of apps elevated by EPM using the default tokens.

    Then tag along in the release notes for features and fixes, updating the EPM alone does not enable Agent Protection, you will have to be on a version that has this feature available and enable that within you EPM Policy. https://docs.beyondtrust.com/epm-wm/docs/policy-editor-utilities#agent-protection-settings
    Jens


    4 replies

    Pulitros144
    Veteran
    December 8, 2025

    @JohnN24 The best way is always to update your EPM agent to the lastest version. 

    PS
    Guru
    December 8, 2025

    As stated in the BT-23-08, Make sure that Anti-Tamper is enabled and also that you have Agent Protection enabled.

    As this will require true local Admin the Agent Protection is key for avoiding Admin users to gain access also, Anti-Tamper will take care of apps elevated by EPM using the default tokens.

    Then tag along in the release notes for features and fixes, updating the EPM alone does not enable Agent Protection, you will have to be on a version that has this feature available and enable that within you EPM Policy. https://docs.beyondtrust.com/epm-wm/docs/policy-editor-utilities#agent-protection-settings

    Jens


    JohnN24Author
    Apprentice
    December 8, 2025

    Where is anti-tamper configured?

    Guru
    December 9, 2025

    Hey John.

    Any access token that you provide in the application rules comes with Anti-Tamper enabled, with the exception of the Privilege Management Support Token, as it need to access policy and the EPM client components.

    This is where you can customize tokens and on the App rules you will assign them.

    Kind regards

    Jens